Mezinárodní federace hudebního průmyslu (International Federation of the Phonographic Industry) navrhla Evropské komisi zařazení populárního open-source nástroje yt-dlp na evropský seznam 'padělků a pirátství' (EU Counterfeit and Piracy Watch List) pro rok 2027 (plné znění žádosti IFPI). IFPI ve svém podání označuje tento aktivně vyvíjený a o rozličné funkce bohatší fork youtube-dl za 'závažný problém' pro hudební průmysl, v
… více »Byla vydána nová verze 7.4 linuxové distribuce Parrot OS (Wikipedie). Jedná se o linuxovou distribuci založenou na Debianu a zaměřenou na penetrační testování, digitální forenzní analýzu, reverzní inženýrství, hacking, anonymitu nebo kryptografii. Přehled novinek v příspěvku na blogu.
Dnes startuje desátý ročník oblíbené kyberbezpečnostní soutěže The Catch organizované Forenzní laboratoří CESNETu. Letos zavede soutěžící do světa národních výzkumných a vzdělávacích sítí (NREN). Čekají na vás tematické úlohy založené na principu Capture the Flag (CTF), hledání ukrytých flagů i zajímavé ceny. Otestujte své schopnosti a vyrazte na lov flagů.
Byly zpracovány a na YouTube zveřejněny videozáznamy z konference LinuxDays 2026.
Německý startup Aleph Alpha k příležitosti výročí sjednocení Německa zveřejnil open-weight jazykový model Kolibri, vyvíjený s ohledem na unijní pojetí autorského práva, ochranu osobních údajů GDPR a nařízení EU o umělé inteligenci, jehož 'Kodexu správné praxe' je Aleph Alpha signatářem. Výsledkem tohoto přístupu je transparentnější technologie, kterou například budou moci využívat evropské veřejné instituce, ovšem za cenu
… více »Nvidia zveřejnila návrh nové bezpečnostní platformy pro nasazování AI agentů. Jedná se o nasazení AI za použití OpenShell a Sentry, dvou oddělených bezpečnostních vrstev, v nichž může Sentry monitorovat a vyhodnocovat chování AI v OpenShellu tak, že ho v krajním případě až vypne. Mělo by to zabránit dalším únikům AI ze sandboxu.
Přímý přenos (YouTube) z konference LinuxDays 2026, jež probíhá tento víkend v Praze v prostorách FIT ČVUT. Na programu je spousta zajímavých přednášek.
Byla vydána nová verze 0.17.0 programovacího jazyka Zig (Codeberg, Wikipedie). Přispělo 206 vývojářů. Přehled novinek v poznámkách k vydání.
Open-source projekt OpenDLSS-NR je 'bitově přesná reimplementace' neuronové rendrovací sítě DLSS 5 od společnosti NVIDIA, jenže pro grafické API Vulkan (DLSS slouží k vylepšování klasickým způsobem vyrendrovaných snímků pomocí lokálních modelů umělé inteligence, a to v reálném čase). Projekt není nijak spojen se společností NVIDIA, je pouze pro OS Windows a natrénované váhy modelu si uživatelé musí obstarat sami. Zdrojový kód je k dispozici na GitHubu, pod licencí MIT s výjimkou pro komponenty třetích stran.
Společnost Cloudflare představila Clef a Clef-Flash, open-source rozhodovací modely určené pro rychlou a konzistentní klasifikaci vstupů. Na rozdíl od klasických LLM vracejí tyto modely deterministické striktně typované strukturované odpovědi s exaktními pravděpodobnostmi, tedy odpovědi ve stylu přelomového modelu Jev.
… více »
29.4.2008 21:31
| Přečteno: 1449×
| Linux
| 
Author: Vladimír Beneš (AToL - PV208, FI.MUNI)
Piranha is a part of Red Hat Cluster Suite and is responsible for IP Load Balancing. IPLB provides the ability to load-balance incoming IP network requests across a farm of servers.
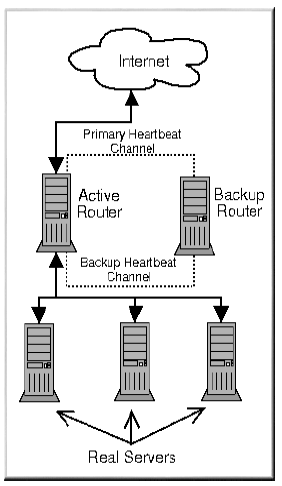
IP Load Balancing is based on open source Linux Virtual Server (LVS) technology, with significant Red Hat enhancements.The IPLB cluster appears as one server, but, in reality, a user from the Web is accessing a group of servers behind a pair of redundant IPLB routers. An IPLB cluster consists of at least two layers. The first layer is composed of a pair of similarly configured Red Hat Enterprise Linux AS or ES systems with Red Hat Cluster Suite installed. One of these nodes acts as the active IPLB router (the other acts as a backup), directing requests from the Internet to the second layer >> a pool of servers called real servers. The real servers provide the critical services to the end-user while the LVS router balances the load to these servers.
The IPVS code provides the controlling intelligence. It matches incoming network traffic for defined virtual servers and redirects each request to a real server, based on an adaptive scheduling algorithm. The scheduler supports two classes of scheduling, each with a weighted and non-weighted version. There is a basic Round Robin scheduler that simply rotates between all active real servers. The more complex scheduler, Least Connections, keeps a history of open connections to all real servers and sends new requests to the real server with the least number of open connections.
IPVS supports three types of network configurations. Network Address Translation (NAT), Tunneling and Direct Routing. NAT requires that there be a public address for the virtual server(s) and a private subnet for the real servers. It then uses IP Masquerading for the real servers. Tunneling uses IP encapsulation and reroutes packets to the real servers. This method requires that the real servers support a tunneled device to unencode the packets. Direct routing rewrites the IP header information and then resends the packet directly to the real server.
Each service running on a real server being routed to as a part of a virtual server is monitored by a nanny process running on the active IPVS router. These service monitors follow a two-step process. First, the hardware/network connectivity is checked to ensure that the real server is responding to the network. Second, a connect is sent to the port of the real server that has the monitored service running on it. Once connected, nanny sends a short header request string and checks to make sure that it receives a banner string back. This process is repeated every two seconds. If a sufficient time (configurable) elapses with no successful connects, the real server is assumed dead and is removed from the IPVS routing table. Nanny continues to monitor the real server and when the service has returned and has remained alive for a specified amount of time, the server's place in the IPVS routing table is restored.
The IPVS router is a single point of failure
(SPOF) so support for a hot standby node is
supported. When configured with a standby, the
inactive machine maintains a current copy of the
cluster's configuration file (/etc/lvs.cf) and
heartbeats across the public network between it
and the active IPVS router node. If, after a
specified amount of time, the active router fails to
respond to heartbeats, the inactive node will
execute a failover. The failover process consists
of recreating the last known IPVS routing table
and stealing the virtual IP(s) that the cluster is
responsible for. The failed node should return to
life, it will announce its return in the form of
heartbeats and will become the new inactive hot
standby IPVS router.
Currently, Piranha only supports the NAT networking model of the IPVS code. The other significant limitation of Piranha is the filesystems. Currently static content on the servers is required. Any dynamic content must come from other shared filesystems or backend databases. For most web sites, the page content is mostly static with CGI activities and dynamic content being pulled from databases.
The primary supported services within a Piranha environment are Web and FTP servers. With the NAT model, the real servers can be any operating system on any hardware platform. The dynamic weight adjustment capabilities are not usable on OSes that do not support rsh (or similar) logins to acquire CPU loads.
The number of real servers that can be supported is theoretically limitless; however, network limitations can be reached with eight to twelve servers, depending on the network connectivity and the server data types. Static FTP content reaches network limitations sooner than dynamic CGI web content.
Tiskni
Sdílej:


 AbcLinuxu.cz
 ITBiz.cz
 HDmag.cz
 AbcPráce.cz
